 Secure by Design
Story Cards
The Secure by Design Story Cards are a deck of 90 cards about why insecure software keeps shipping, who pays the price, and what it would take to change that. Each card has a front that makes a point and a back that asks questions.
Use them alone or with a team. Draw a card, think about how it applies to your role, and start a conversation. The deck is written for people who build software, people who buy it, and people who shape the incentives around both. All 90 cards are here.
The Story Cards are licensed under a Creative Commons Attribution-NonCommercial 4.0 International license (CC BY-NC 4.0). You may share and adapt them for non-commercial purposes, as long as you give credit to Robert Lord, link to the license, and say whether you made changes.
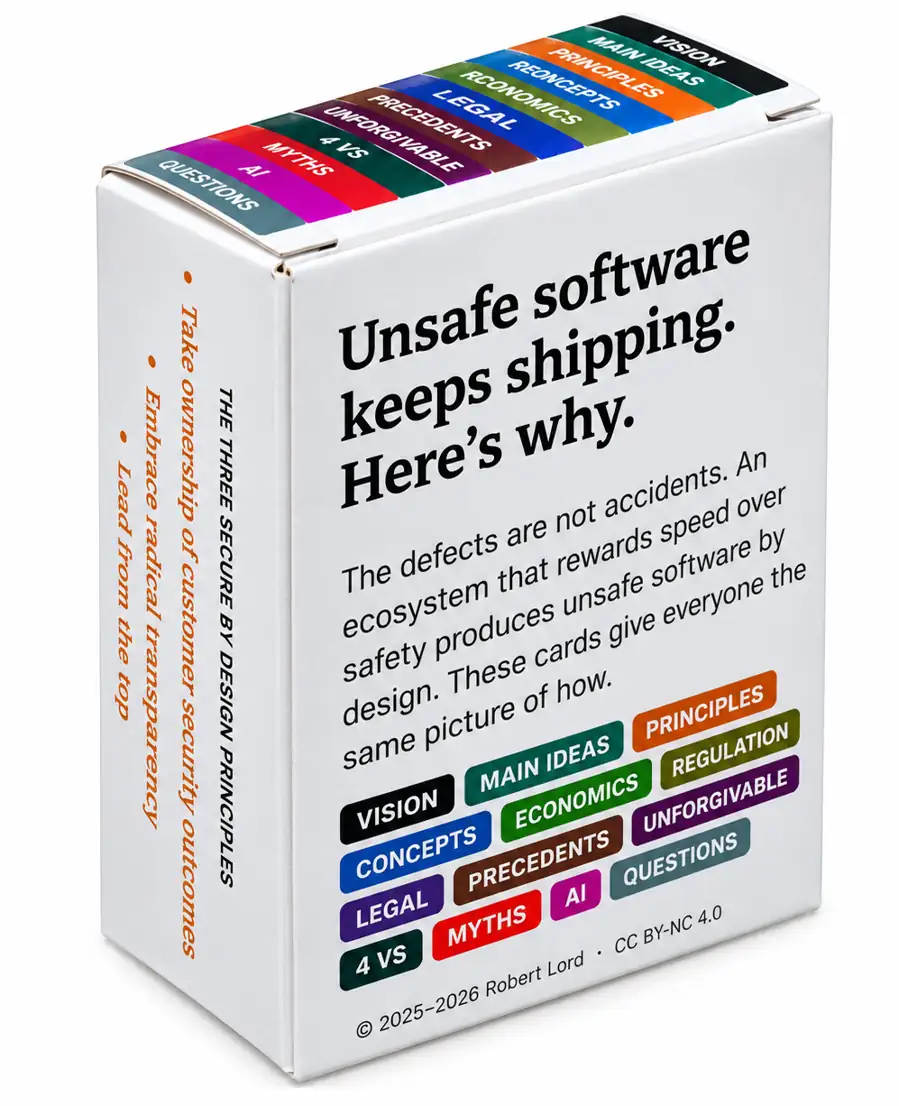
Prefer paper?
The Story Cards come as a boxed, printed deck, ready for a workshop, a team meeting, or your desk.
Buy the printed deckWelcome
Vision
Harm
Main Ideas
Principles
Concepts
- C-01Near Misses
- C-02Classes of Defect
- C-03Software Quality
- C-04Language Matters
- C-05Memory Safety
- C-06Human Error
- C-07Immediate & Root Causes
- C-08Threat Modeling
- C-09CVE
- C-10Customer Field Studies
- C-11Tightening & Loosening
- C-12Vulnerability Disclosure Policy
- C-13SBOMs
- C-14Liability
- C-15Manufacturers vs. Operators
- C-16Research Chilling Effects
- C-17Licensed Professions
- C-18Risk-Informed Decision
Economics
Legal
Regulation
Precedents
Unforgivable
4 Vs
Myths
- M-01“Our products are not targets”
- M-02“Security stifles innovation”
- M-03“A secure laptop will cost $10k!”
- M-04“Security breaks usability”
- M-05“Our products are already SbD”
- M-06“We already have frameworks”
- M-07“AI will fix security”
- M-08“Orgs just need to patch faster”
- M-09“Attackers keep adapting”
- M-10“It was a sophisticated attack”